- Home
- Technical Solutions
- Technical Publications
- Grid Business
- Announcements
- Grid Middleware
- Existing Grids
- Grid Links
- Feedback
The Policy Decision Point takes decisions based on the attributes owned by the user and a set of policies; it interacts with the Policy Enforcement Point to provide the taken decision.
The Policy Decision Point needs to be adopted when the access to files or other resources on a computer network should be granted by a policy-based access management system.
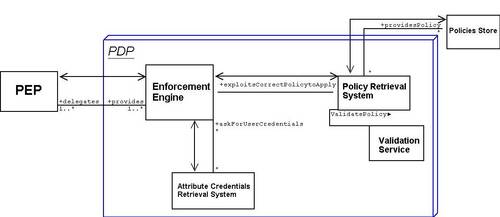
The PEP generates the AuthzDecisionQuery, and sends it to the PDP.
Attribute/Policy Retrieval System A PolicyQuery is sent from the PDPEngine to the Policies Store Manager in order to obtain one or more set of policies. The query may include the values of subject attribute, resource attribute, action attribute and other parameters. The PolicyStatement is used by the Engine to return a policy or a policyset in a response to the PolicyQuery request
Validation Service provides validations for the signed policies and eventually Attribute Credentials owned by the user.
Enforcement Engine evaluates policies and credentials; an AuthzDecisionStatement is generated and sent to the PEP as a response.
Attributes Credentials and Policies could be stored locally or in distributed manner (LDAP directories for instance).
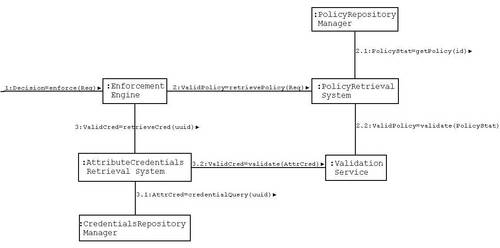
When the PEP requires a policy decision it contacts the PDP for a policy decision. The request contains elements which can be used by the PolicyRetrievalSystem to locate the correct policy to apply. The policy is signed and needs to be validated by the ValidationService. In order to grant the access to a specific resource the policy could require the evaluation of a set of user attributes, these attributes could be embedded in credentials owned by the user and issued by appropriate Attribute Authority recognized by the issuer of the policy.
 Print this page