- Home
- Technical Solutions
- Technical Publications
- Grid Business
- Announcements
- Grid Middleware
- Existing Grids
- Grid Links
- Feedback
The aim of this pattern is to ensure trust between different entities that are collaborating through the grid.
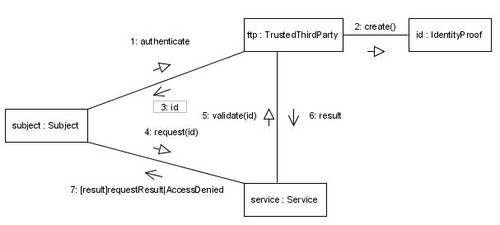
The trust between entities in a network of peers is not easy to ensure. Indeed, a way to solve this situation is to use a trusted third party in order to validate the identity of the others entities of the system. This entity is in charge of creating an identity proof for a subject entity (client of a service) and to validate this entity when a service receives a request from this subject entity.
This pattern can be applied when trust must be ensured between the different entities of a distributed system. This pattern is useful in grid architecture and also in service oriented architecture.
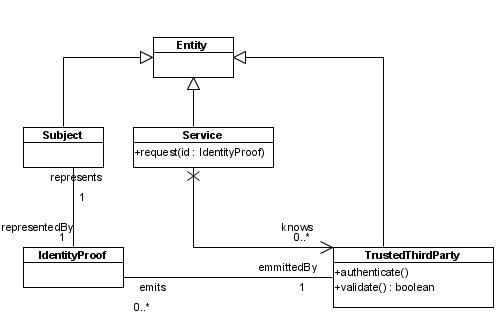
The subject is an entity of the distributed architecture that wants to perform a service. The subject needs to be authenticated by the service.
The service is the entity that provides an operation for trusted subject. A service needs to receive a proof of identity when a subject invokes his operations.
The identityProof is the proof of the identity of a subject emitted by a trusted third party.
The TrustedThirdParty is an entity in charge to give an identity proof of an entity. This entity must be trusted by the entities of the system.
Before performing a request (on operation from a service), the subject authenticates by the third party. The third party gives a proof of the identity of the subject. Then, the subject makes his request to the service providing his identity proof. The service checks by the third party if the identity is trusted. If it is trusted the service sends the result of the operation. If not, an access denied error occurs.
 Print this page