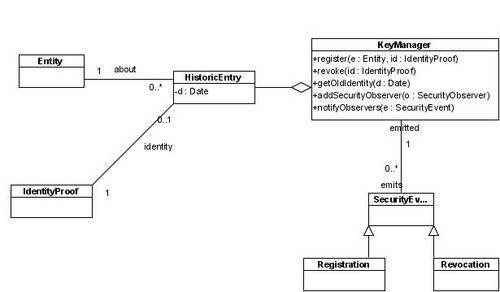
The aim of this pattern is to solve the problems linked to managing identity material. Indeed, the identity of an entity can evolve during time (it can be revoked, changed )
In some situations, an identity of an entity can evolve by example it can be revoked. Sometimes some data encrypted by this entity must be decrypted. In this situation, a key manager is useful to retrieve old identity in order to decrypt the data.
This pattern is useful when keys can evolve during time and old data must be retrieved. Its also useful to manage entities identity.